Build your cybersecurity program yourself. Bring us in when you need an outside check.
The BrainTrust is our membership for SEC-registered firms. Start with a free account. Premium, at $2,500 a year, gives you guided tools and templates to build your own cybersecurity policies, incident plan, vendor file and training records. When you want an outside test of what you built, Premium members can book one from us at a set price.
- Step 1 Free account Free Our Securing Compliance exam report, the mock SEC exam, a document review checklist and every article. Name and email, no card. Compare Free and Premium
- Step 2 Premium $2,500 / year The do-it-yourself tools: your Policies & Procedures Manual, vendor portal, 60 templates, training records, incident response tools and a quarterly external scan. See the Premium tools
- Step 3 Outside testing, when you want it Premium members · from $2,500 Extra, at set prices. We test or review part of your program and give you a written report for your exam file. See the engagements
In an SEC or FINRA exam right now? Premium members can add Examination Response Support ↓
Two tiers. One Premium price.
Free puts real material in your hands today. Premium is the full library and the tools that build your documents: $2,500 a year, flat. Cancel anytime; there are no refunds, and access continues to the end of the paid year.
The BrainTrust
A practical starting point for firms that want direction before building a more formal cybersecurity compliance program.
- Securing Compliance: what SEC examiners ask for
- Mock SEC Cyber Exam: 30 real request-list items, scored
- Cybersecurity Compliance Document Review Matrix
- SEC Exam Cybersecurity Preparedness Brief
- Reg S-P 2024 Compliance Impact Summary
- Employee Technology Use Policy template
- Every Insight: cybersecurity commentary and SEC enforcement updates
The BrainTrust Premium
For firms that will do the work themselves. You answer the questions, confirm the facts and keep the documents current; the tools do the drafting. Once you are set up, plan on about 3 to 4 hours a quarter, including your own FieldCraft training.
- Policies & Procedures Manual Builder
- Incident response plan builder and incident record tool
- Vendor due diligence portal: 600+ researched vendors
- FieldCraft staff training for up to 50 users
- 60 editable templates, each tied to the rule it supports
- AI governance kit
- Quarterly outside scan of your website and email domain
- Email questions answered by the people who wrote the materials
- Outside testing available at set prices (see below)
- Everything in the Free tier
By subscribing you agree to the BrainTrust Member Policy.
Your written program, your vendor file, and the rest of the evidence.
Most firms come for the vendor due diligence portal and the Policies & Procedures Manual. Premium packages them with the other records an SEC-registered firm is asked to show: that it trains its people, can respond to an incident, and has written its policies. You use the tools; you own the program and the evidence file.
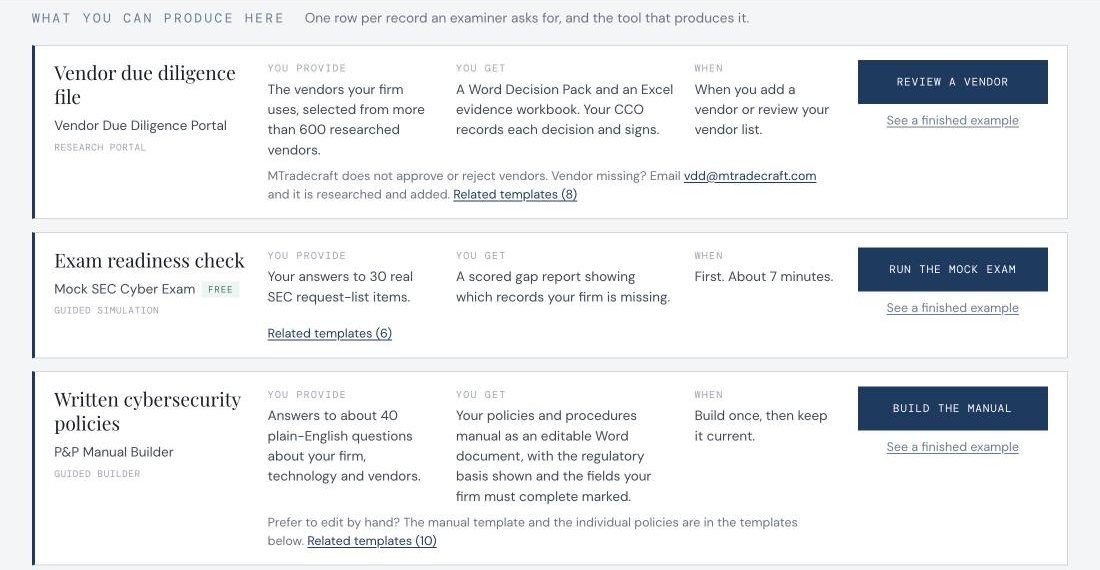
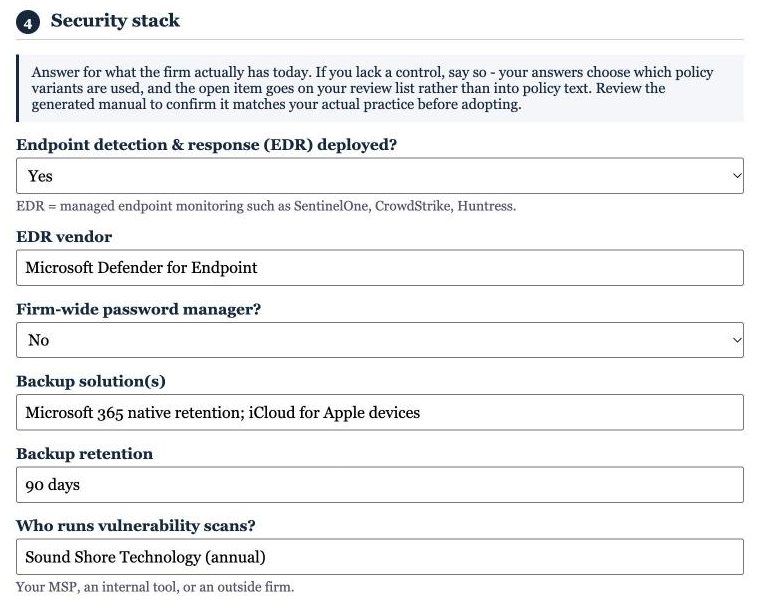
The Reg S-P vendor file, already researched. You decide and sign.
Search 600+ vendors RIAs actually use. Each record has a plain-language summary and every answer with its source and the date we checked it. Anything we could not confirm from a public source is marked Unknown. If a vendor says it has a SOC 2 report but keeps it private, the record says so; to read the report itself, you request it from the vendor. Select the vendors your firm uses and export the decision pack: one summary page across every vendor, one decision sheet per vendor, and an Excel workbook of the same evidence. We supply the research; your CCO records the decision and signs.
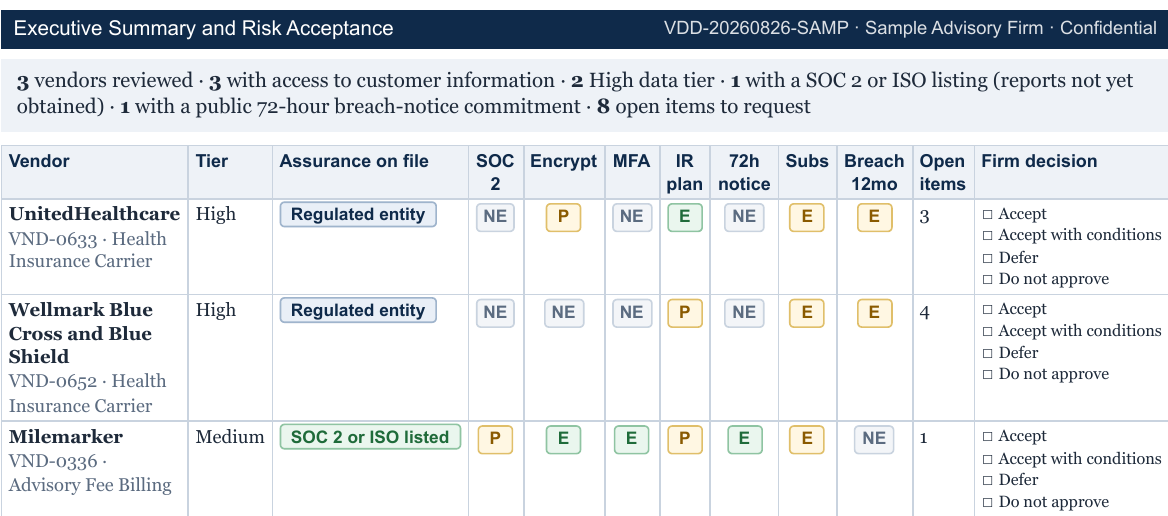 The executive page of an exported decision pack (sample firm, three vendors).
Vendor missing? Email vdd@mtradecraft.com and we research it, forward the vendor our self-report form, or send us their SOC 2 report or ISO certificate.
Your written cybersecurity program, built from your answers
Answer questions about your firm, your people and the systems you use. The P&P Manual Builder writes your firm's cybersecurity policies and procedures manual as an editable Word document, each section mapped to Reg S-P, Rule 206(4)-7 and Rule 204-2. It also emails you an answers file, so next year's update starts from this year's answers.
Security awareness, with the records
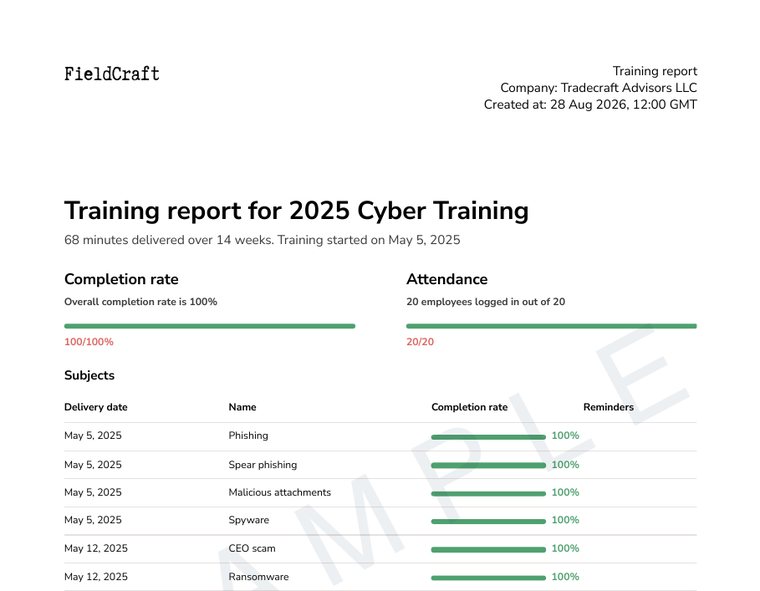
Phishing simulations, quiz tracking, and audit-ready completion reports for up to 50 employees, the training evidence that supports your Reg S-P safeguards program.
The plan before, the record during
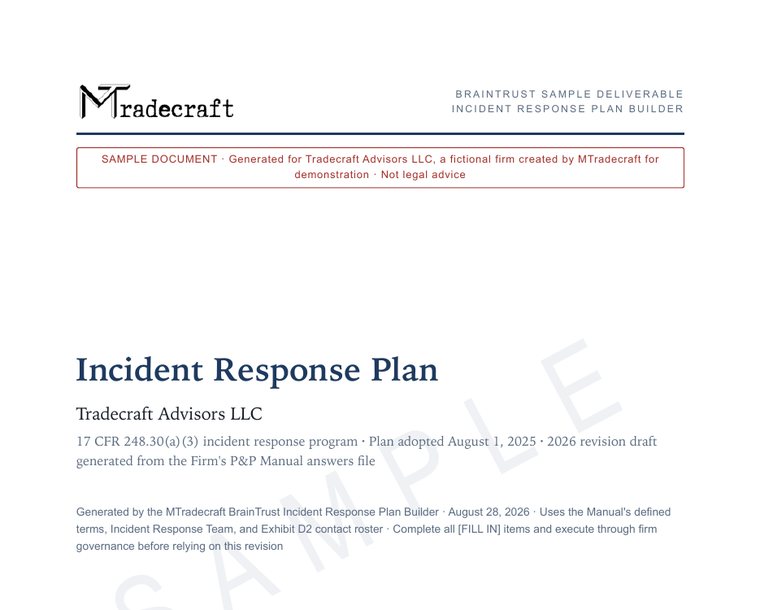
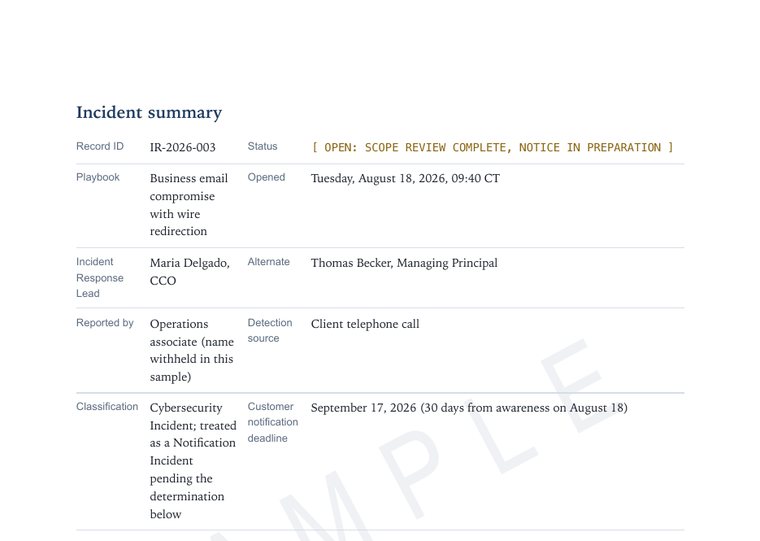
Answer five minutes of questions; the IRP Builder generates your firm-specific Reg S-P incident response plan as an editable Word document, every section mapped to the Reg S-P incident response rule. If an incident starts, the Incident Response Assistant is a guided tool that records each step and decision your team makes, with timestamps, for your Reg S-P and Rule 204-2 files. It keeps the record; it is not an incident response service.
Document how your firm governs AI
The AI Compliance Framework, governance workbook, output validation protocol, and AI marketing claims checklist, plus an AI supplemental track inside the vendor portal.
What anyone on the internet can see about your firm, every quarter
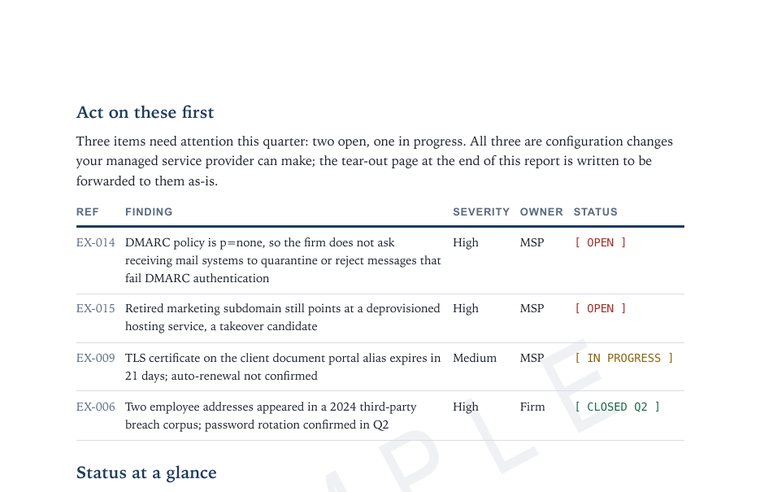
We check your website and email domain from the outside: fake look-alike web addresses, old pages left online, email settings that let someone pretend to be you, and staff passwords exposed in public data breaches. You get a short written report every quarter. Nothing to install and no access to your systems; tell us your domains once. It does not test your office network or cloud accounts.
Real output from the Premium tools, generated for Tradecraft Advisors, a fictional firm we use for samples. See every sample →
When you want someone outside the firm to check the work.
Premium gives you the tools to build the program. These one-time engagements test what you built, and each ends with a written report for your exam file.
Our tests measure your firm against the policies, plans and vendor records you build in Premium, so the report reflects your actual program. That is why these engagements are for Premium members.
Subscribe to Premium, then email us which engagement you want. We confirm the scope and price in writing before any work starts. We test and document; your IT provider makes any changes.
Full Cybersecurity Audit
“If an examiner asked to see proof our safeguards work, what would we hand them?”
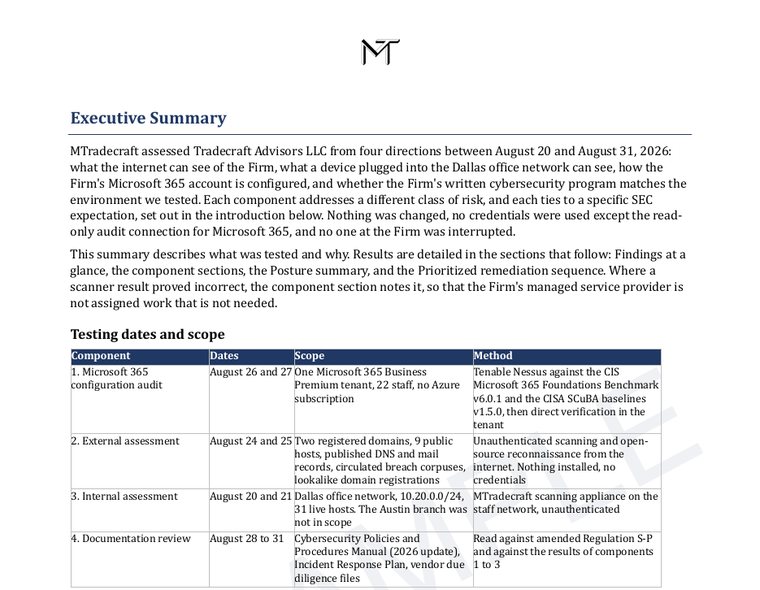
Five parts, run together as one engagement. You receive one report that ties every finding to the SEC rule it affects, plus a step-by-step task list to hand to your IT provider. The price covers one office, one primary domain and one cloud system. When your firm moves quickly, start to finish takes about 10 business days. Each part can also be booked on its own at the price shown.
-
1
Internal test (Internal Office Check)$2,750per office, on its own
We mail you a small device that checks the computers, servers and printers on your office network for missing updates and weak settings, then you mail it back. This part needs an office network. For a fully remote firm it usually does not apply: we can test a home network only when it is kept separate for work, and we generally do not recommend it.
-
2
External test (External Office Check)$2,500per office, on its own
We test your office internet connection, firewall and remote access from the outside, the way someone on the internet would try to get in.
-
3
Cloud test (one cloud system you choose)$2,500–$4,100on its own
Pick the system that holds the most client information. We check its security settings against a published standard, using read-only access your IT provider sets up: who can sign in, what each user can see and export, and how activity is recorded.
- Microsoft 365$4,100 ($4,500 with laptop and phone settings)
- Microsoft Azure$2,500 per account
- Salesforce, Zoom, AWS or Google Cloud$2,500 each
In the Full Cybersecurity Audit: your first cloud system is included. Each additional cloud system in the same audit is $1,000.
-
4
Policy review (Policies & Procedures Review)$5,000on its own
We read the policies, incident response plan and vendor procedures you built and compare them with current SEC exam priorities and how your firm actually works, including staff use of AI tools. You receive a gap list with suggested wording.
-
5
Written risk and threat assessmentIncludedwith Premium
What anyone on the internet can see about your firm, written up against Reg S-P and Reg S-ID. You already receive this every quarter with Premium, so it costs nothing extra; the audit puts the latest one into the same report so you have one complete file.
Also for Premium members
| Engagement | What you receive | Fee |
|---|---|---|
| Incident Plan Response Review “Would our incident response plan actually work if something happened?” |
A tabletop exercise, available after your firm has completed a Full Cybersecurity Audit. We build a scenario from your audit results and run it remotely with your named response team against your own plan. You receive a written after-action report for your incident response program file. | $5,000 |
| Follow-Up Test “Our IT provider says it is fixed. Can we prove it?” |
After your IT provider works through the task list, we re-test the original findings and document what is closed and what is still open, for your exam file. | $1,250 |
Prices cover one office, one account per service (Microsoft 365 up to 50 users) and one primary domain. Anything larger is quoted in writing before work begins. We test and document; your IT provider makes the changes. Cloud tests need read-only access set up by your IT provider.
Consulting and examination support
AI Consulting
Help putting your firm's AI governance in place: an AI use policy that fits how your staff actually use AI tools, review of the AI features in the vendors you rely on, output review procedures, and marketing claims that mention AI. Built on the AI governance kit in your library.
$300 an hour · 40-hour minimum
Examination Response Support
Help during a live SEC or FINRA examination: assembling and indexing the cybersecurity production set, flagging inconsistencies before submission, drafting cybersecurity responses for your CCO and counsel to approve, and joining examiner calls on request. Not a member yet? Subscribe to Premium, then email us and we will set up the engagement.
$5,000 engagement fee, plus $300 an hour
Retainer support
For firms that want the program operated for them or ongoing security leadership support, retainer arrangements are available by request. Scope and cadence are set in a written engagement after a short call.
By request
The same materials our engagements run on.
Built in practice, not for the shelf
Premium is the library and tools our own engagements are built on. When a Premium member books an engagement, we test against the same documents the member already has.
They are written by Brian Hahn, who carried chief compliance officer responsibilities at SEC-registered firms and took a firm through an SEC examination with no material findings. Every template cites the rule it supports (Reg S-P, Rule 206(4)-7, Rule 204-2) and is revised as rulemaking and examination priorities move.
Email support from the practice, not a help desk
Premium members email us directly with cybersecurity compliance questions: which template applies, how a rule reads, how to adapt a document to the firm. Answers come from the people who wrote the materials.
It is a resource subscription, not a consulting relationship: no firm-specific drafting, no examination representation, and we cannot be named as your cybersecurity expert or CISO. When you want us to test or review something, that is an à la carte engagement.
Maintained as the rules change, and cited to them.
Every template cites the specific rule it supports and the library is revised as SEC rulemaking and examination priorities move, so the version you download reflects current requirements.
Cybersecurity Policies & Procedures Manual (Reg S-P), NPI Data Inventory, Access Control & MFA, Annual Risk Assessment, Data Disposal.
Incident Response Plan, Tabletop Exercise Kit, Wire-Transfer & Disbursement Verification, plus the interactive IRP Builder and the Incident Response Assistant for use during an incident.
AI Compliance Framework & Governance Workbook, AI Output Validation Protocol, AI Marketing Claims Review Checklist.
Vendor Due-Diligence Questionnaire and Confidentiality Agreement, alongside the 600-vendor evidence portal.
206(4)-7 Annual Review, Compliance Calendar, Compliance Meeting Agenda.
Code of Ethics, Conflicts of Interest, Gifts & Entertainment, Political Contributions, Outside Business Activity.
Client Communication Letter Suite, Form ADV Amendment Checklist, Reg S-ID Red Flags.
Marketing Procedures Policy, Firm & Employee Social Media Policies, Promoter & Solicitor Oversight.
Best Execution Evaluation, Trade Error Policy & Log, Proxy Voting, Custody Rule Compliance Checklist.
Employee Technology Use Agreement, Whistleblower Policy, and acknowledgement forms.
Business Continuity Plan, Books & Records Policy, Written Supervisory Procedures.
SEC Exam Document Production Checklist, First-Time Examination Guide, Cybersecurity Request Bundle.
60 editable templates across 13 categories, each mapped to the rule it supports. Browse the full library →
Built for firms in a specific situation.
Premium fits if…
- You are a CCO or IT manager at an SEC-registered firm and you need real policy templates, not generic ones.
- You have examination obligations you cannot ignore and want to do the work in-house.
- You have an examination, an insurance renewal or a client due diligence questionnaire on the calendar and need the written program and evidence file in place first.
- You built the program and now want an outside test of it. Premium plus one à la carte engagement covers that.
Premium is not the right fit if…
- You need someone else to operate the cybersecurity program, or an insurer or client questionnaire requires named security leadership. That is a retainer, quoted on request.
- You are a compliance consultant who wants to use the library in paid work for your own clients. Membership is licensed for one firm's internal use; consultants are served under a separate Consultant license.
Questions firms ask before subscribing.
Can we book an audit without a Premium membership?
No. À la carte engagements, AI consulting and Examination Response Support are available only to BrainTrust Premium members. Premium gives your firm the policies, plans and records that the engagement then tests against, so the report reflects your program rather than a blank page.
How much does cybersecurity compliance cost for an RIA?
A BrainTrust Premium membership is $2,500 a year. Premium members can add the Full Cybersecurity Audit for $9,000, or book its parts on their own: $2,750 per office for the internal test, $2,500 per office for the external test, $4,100 for a Microsoft 365 cloud test ($4,500 with laptop and phone settings), $2,500 for an Azure, Salesforce, Zoom, AWS or Google Cloud test, and $5,000 for the policy review. Within the audit, each cloud system after the first is $1,000. Members can also add an incident plan response review ($5,000, after a completed audit), a follow-up test ($1,250) and AI consulting ($300 an hour, 40-hour minimum). Members in a live examination can add Examination Response Support: a $5,000 engagement fee plus $300 an hour. Retainer arrangements are quoted on request.
What is the Full Cybersecurity Audit?
Our most complete one-time engagement for Premium members, made of five parts: an internal test of your office network, an external test of your office connection, a cloud test of one system you choose (Microsoft 365, Azure, Salesforce, Zoom, AWS or Google Cloud; each additional system in the same audit is $1,000), a review of your written policies, and a written risk and threat assessment. You receive one report that ties every finding to the SEC rule it affects, plus a task list for your IT provider. When your firm moves quickly, start to finish takes about 10 business days. It is $9,000, against $14,350 for the same parts booked separately with Microsoft 365.
Is Premium enough on its own?
Premium is enough to build and keep your documentation if someone at your firm is responsible for doing the work. It does not test your office network or cloud settings, and no one outside the firm checks the file. When you want that, members add an à la carte engagement.
How much time does Premium take?
Setting up takes the most time: answering the builders' questions, adopting the documents and enrolling staff in training. Once you are set up, plan on about 3 to 4 hours a quarter, including your own FieldCraft training. Premium is $2,500 a year; you can cancel anytime, there are no refunds, and access continues to the end of the paid year.
Can you run the cybersecurity program for us?
For firms that want the program operated for them or ongoing security leadership support, retainer arrangements are available by request. Scope, cadence and fee are set in a written engagement after a short call; there is no standard package.
Cancellation, customized documents, FieldCraft seats beyond 50 users, client data, timelines and retests: see all questions.
Start free. Add Premium when the work is real. Add a review when you want it checked.
Premium is $2,500 a year and starts the moment you subscribe. Upgrade when the exam notice, the insurance questionnaire or a client due diligence questionnaire arrives.
By creating an account or subscribing you agree to the BrainTrust Member Policy.